Security & Compliance Readiness Review
Confirm what you already believe — or find out what needs to change.
You know your business. You may have personally chosen the technology, approved the spending, or watched the current setup take shape over years of growth and change. What you want isn't someone telling you what you got wrong. It's confirmation — that your controls are real, that your documentation would hold up, and that your security and compliance practices still fit the company you run today.
Which situation fits you?
Three reasons companies bring us in
Open the one that sounds like your situation.
Someone outside your company is asking+
A bank or lender is asking questions. A cyber-insurance renewal is approaching. A major customer has sent a questionnaire, an auditor needs evidence, or a new regulatory requirement applies. Each one means someone wants security and compliance information from you. You need accurate answers, supporting documentation, and help understanding what the questions really mean — including when an attorney, insurance advisor, or other specialist should weigh in.
You want independent confirmation+
Your provider or internal team believes the right safeguards are in place. An outside review confirms whether those safeguards actually hold up, using the same controls, documentation, and evidence leadership is already relying on.
You want to know where the single points of failure are+
A key employee, outside provider, administrative account, aging device or server, or undocumented system may be carrying more of the business than anyone realizes. We identify where access, knowledge, or operations depend on one person, one vendor, or one piece of technology — and where there is no practical backup plan.
What we look at
Depending on which of the above brought you here, this can include:
01Access & identity+
- Microsoft 365 configuration and governance
- Access, MFA, and administrative rights
- Vendor and account ownership
- Administrative accounts and who controls them
02Systems & continuity+
- Backup and recovery readiness
- Endpoint protection and patching
- Email security
- Aging devices, servers, and undocumented systems
03Documentation & key-person dependence+
- Written policies and whether they match actual practice
- Documentation and key-person dependence
- Provider arrangements and what they actually cover
- Evidence that supports the answers you give
04Outside requirements+
- Questionnaire and evidence requirements from cyber-insurance, banks, and customers
- Readiness for applicable requirements such as HIPAA, PCI DSS, or CMMC
- Auditor and lender information requests
We validate the picture through leadership interviews, configuration and access review, policy and documentation review, evidence collection, and, where appropriate, testing of critical controls.
Assessments are led by Jean Prejean, Principal, CISA and CISM certified, with project execution led by Wayne Speziale, Director of Operations, a certified Project Management Professional (PMP).
As part of the review, we also look at whether licensing, subscriptions, vendors, and infrastructure still fit the business. Technology spending often accumulates gradually as companies grow and change; the goal is simply to make sure today's spending supports today's needs.
Why an outside review matters
An outside review validates controls, gathers evidence, and identifies gaps that day-to-day support may not surface. We typically work directly with your current IT provider or internal team throughout the process — this adds a second set of eyes, it doesn't replace anyone.
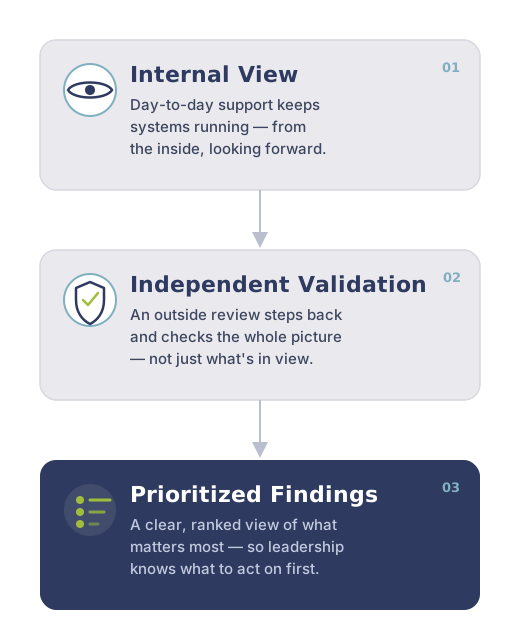
The goal is to independently confirm what's working and identify what deserves attention.
What happens after
You receive a plain-language findings report — including a visual risk heat map showing where concerns cluster by impact and likelihood, so it's clear at a glance what matters most — covering what is already solid, what needs attention, what evidence supports your current answers, and what should happen next.
Illustrative example. Your report reflects what we actually find in your environment.
Beyond the report
A report telling you what to fix is not always the finish line
Depending on what you need, we can also do the work.
Write the policies
Write or update the security and compliance policies a bank, insurer, customer, or regulator expects to see — not just identify what is missing.
Complete the questionnaires
Complete security and compliance questionnaires using the evidence we have gathered, rather than handing you a findings list and leaving the writing to your team.
Keep it current
Keep policies, evidence, training records, questionnaire responses, and key-control validation current from year to year.
The goal is to make the next review routine rather than another scramble. Incomplete, inconsistent, or unsupported answers often lead to more follow-up questions and higher expectations the next time around; staying current is usually easier than rebuilding everything under deadline.
Know exactly what you can put in front of a bank, insurer, customer, or regulator
And where additional work or outside advice is needed.
What this isn't. This is compliance readiness and support — not a legal opinion, formal attestation, or certification of compliance. Where you need an attorney, insurance broker, or certifying body, we'll say so plainly, and we're glad to work alongside them rather than in their place.